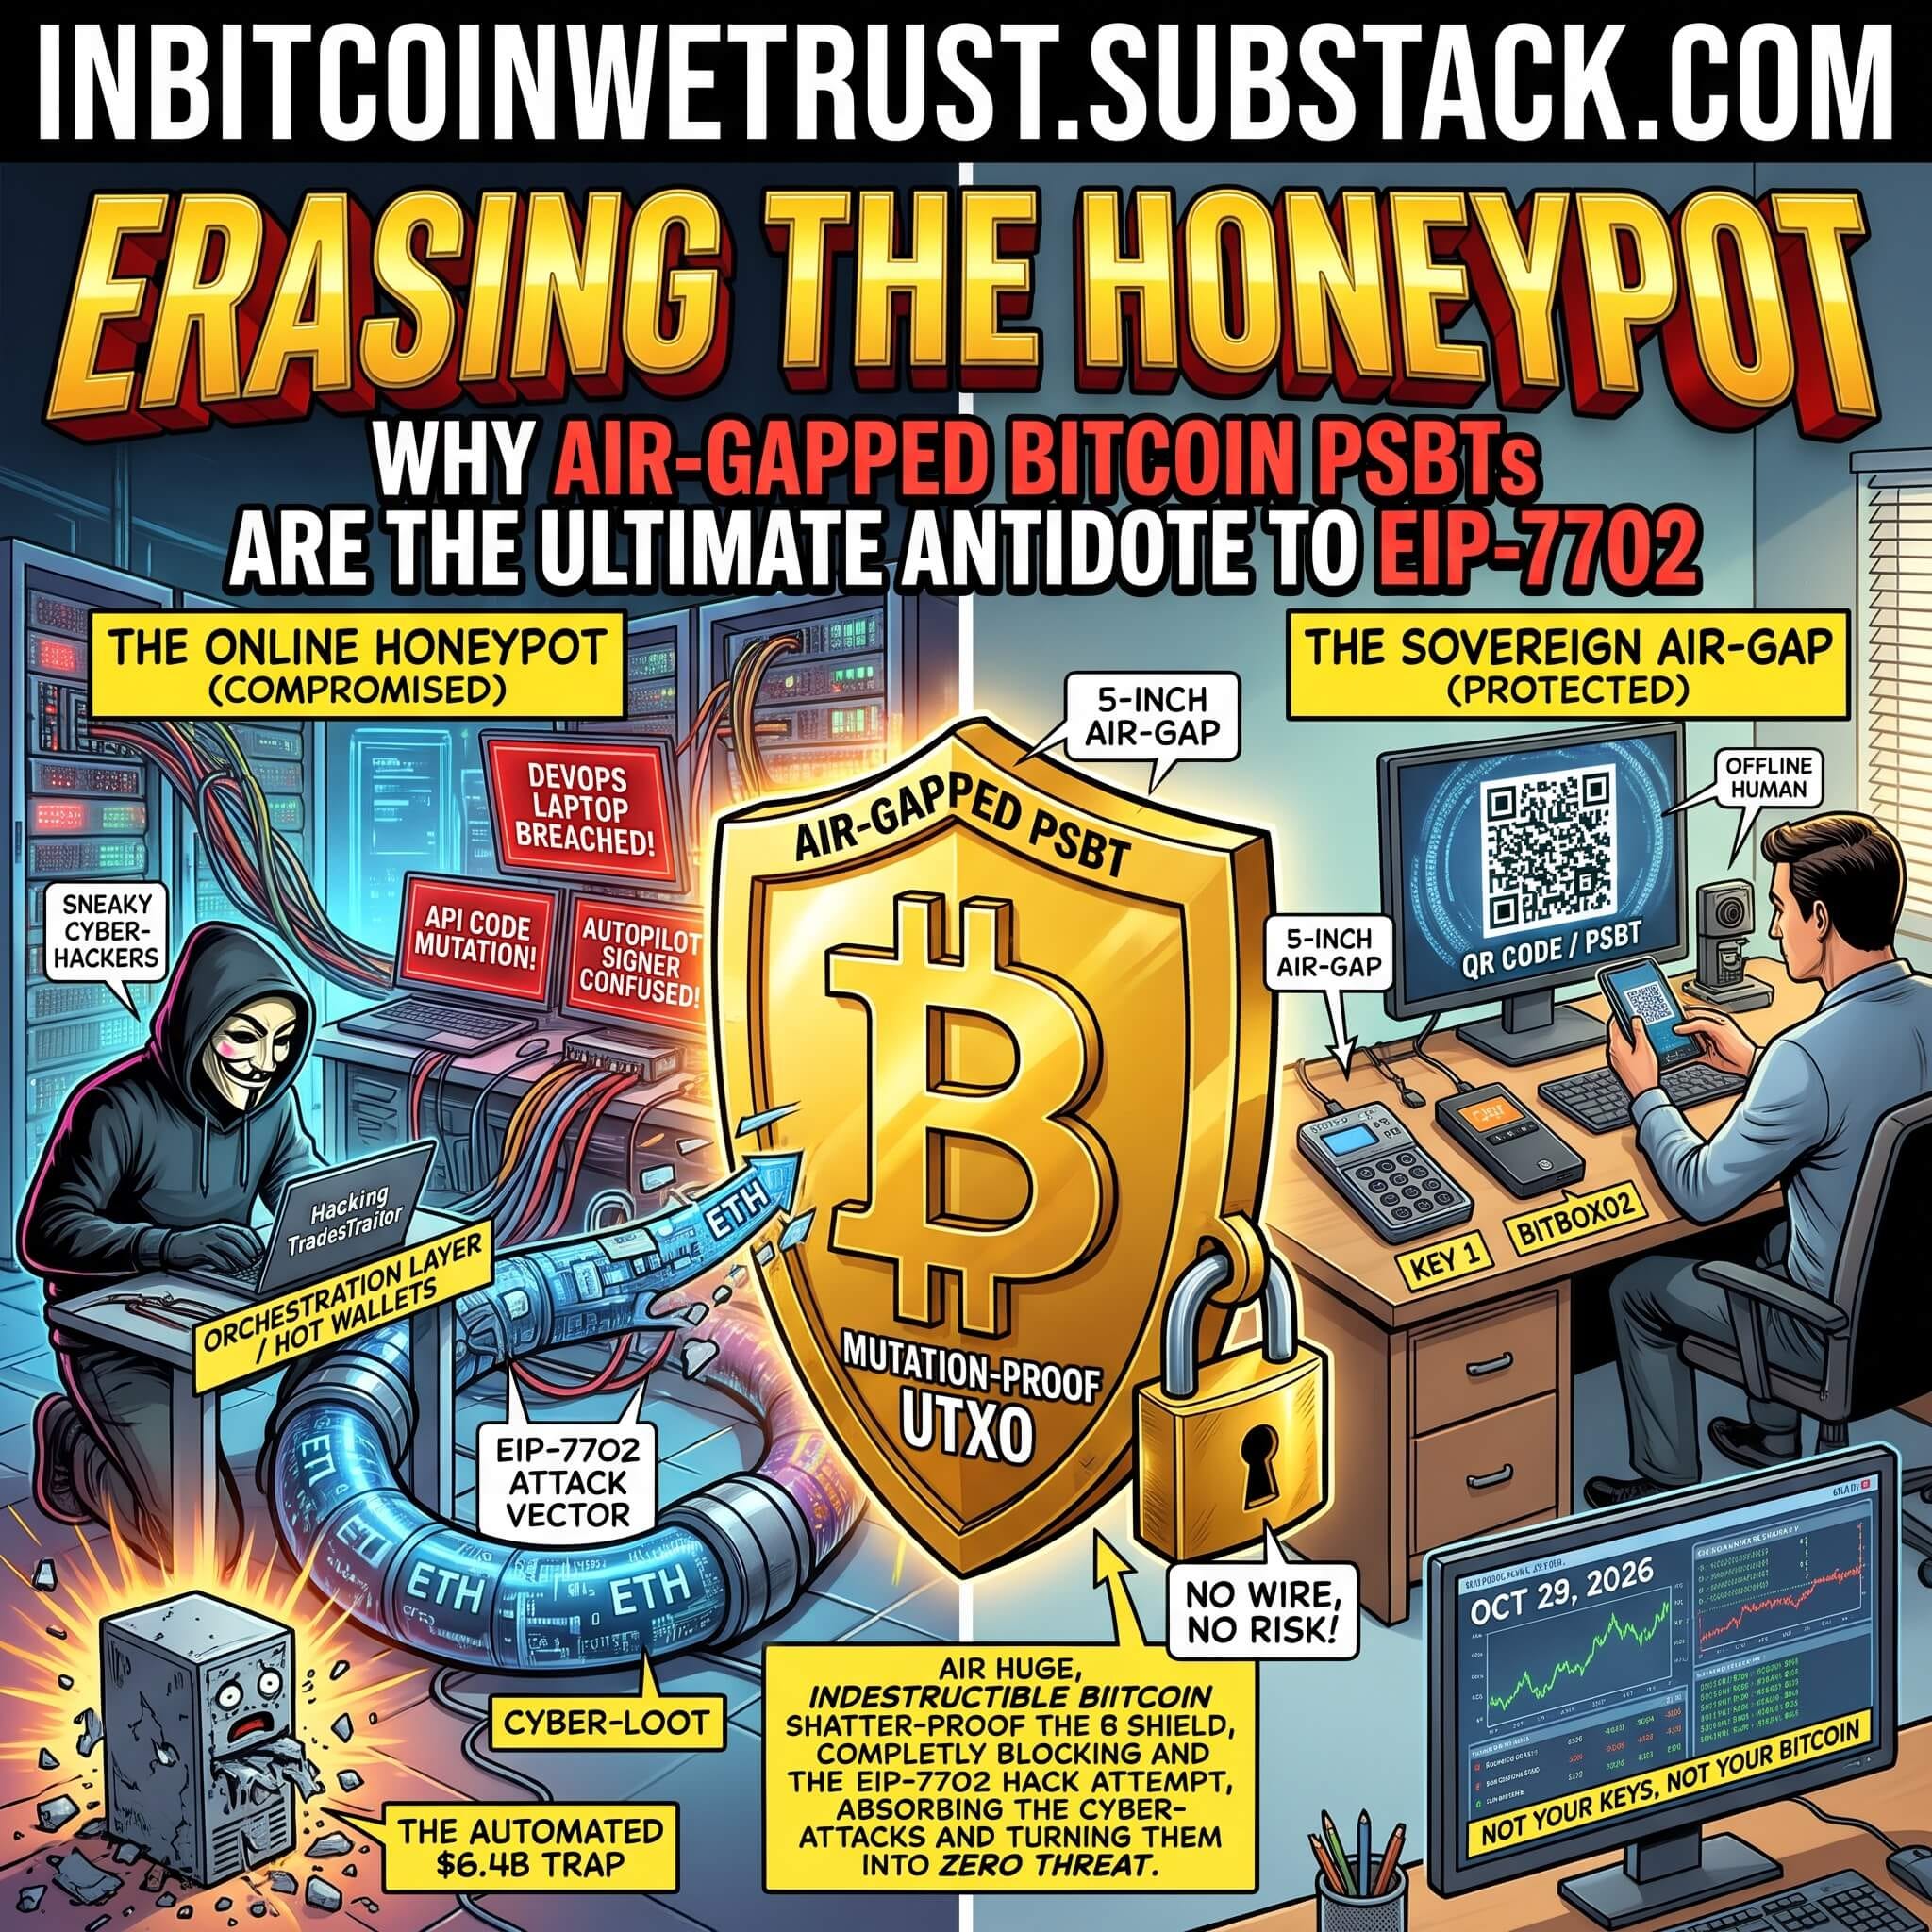
At 20:20:59 UTC on Thursday, October 29, 2026, the conventional wisdom of institutional cryptocurrency custody died inside a cloud server container.
Over the next twenty minutes, operators linked to North Korea’s state-sponsored Lazarus Group executed the largest financial heist in human history, draining $6.36 billion from Binance across ten separate blockchains. Yet when the dust settled the following morning and exchange executives published their preliminary forensic findings, the most chilling detail was not the dollar figure, nor the $1.58 billion liquidation cascade that briefly dragged Bitcoin down toward $76,000.
It was a single, eleven-word sentence buried in the official security report:
“We have found no evidence of any wallet private key leak.”
Pause and absorb the architectural horror of that statement.
For the better part of a decade, the institutional custody industry has spent billions of dollars convincing hedge funds, corporate treasurers, regulators, and retail depositors that the central problem of digital asset security is key extraction.
Protect the raw 256-bit private key inside a military-grade Hardware Security Module or shatter it across three continents using Multi-Party Computation, the sales pitch went, and your vault is impenetrable.
On the night of October 29, the world learned the hard way that an attacker does not need to steal your private key if they can simply instruct your machine to use it.
By compromising a DevOps engineer’s laptop and pivoting into the internal withdrawal service container that feeds unsigned payloads into Binance’s signing enclave, the attackers turned the fortress’s own automated pen against itself.
Worse still, on Ethereum, they weaponized a newly introduced smart-account standard—EIP-7702
—to permanently rewire the exchange’s flagship hot wallet into a self-draining vacuum cleaner that emptied itself three separate times as internal treasury bots dutifully refilled it.
While centralized stablecoin issuers at Tether and Circle scrambled to flip their administrative kill-switches and freeze $3 billion in corporate IOUs, 18,270 Bitcoin—worth roughly $1.45 billion—walked out the front door into a nineteen-address peel chain. Not a single satoshi of that Bitcoin could be frozen, reversed, or bailed out by a corporate compliance desk.
Yet here is the question that almost no mainstream financial journalist has bothered to ask in the aftermath of the catastrophe:
Why were 18,270 sovereign Bitcoins sitting behind an internet-connected, automated API signing pipeline in the first place?
And why did the Bitcoin protocol natively possess the exact cryptographic architecture required to make both the DevOps orchestration hijack and the
EIP-7702
delegation trap completely impossible—an architecture that centralized exchanges systematically choose to ignore?
To understand why the future of institutional and personal wealth belongs to air-gapped PSBTs and multivendor quorums, we must first dissect how modern “smart” hot wallets turned themselves into a $6.4 billion honeypot.
Why did multi-million-dollar Hardware Security Modules and distributed Multi-Party Computation enclaves fail to stop a twenty-minute drain on October 29?
In computer science, the vulnerability that felled Binance’s hot-wallet perimeter is known as the Confused Deputy Problem, driven by a fatal design flaw called ambient authority.
When an enterprise exchange processes tens of thousands of customer withdrawals every hour across a dozen blockchains, human eyes cannot physically inspect every outbound transaction. If an executive had to sit inside a Faraday cage and manually verify fifty thousand destination addresses an hour on a physical screen, the exchange’s withdrawal queue would grind to a halt within three minutes.
To solve for industrial throughput, exchanges replace human verification with an automated signing pipeline consisting of three distinct layers:
**The Orchestration Layer:**Cloud-hosted microservices and Docker containers aggregate user withdrawal requests, check internal SQL database balances, and construct raw transaction payloads.**The Policy Engine:**Automated middleware checks velocity limits, IP whitelists, and internal cryptographic service tokens to verify that the request originated from an authorized internal container.**The Signing Enclave:**The HSM or MPC cluster receives the pre-approved digest over an internal network socket, applies its sharded mathematical secret, and returns a valid digital signature in milliseconds.
Look closely at where the trust lives in that three-tier pipeline.
The HSM or MPC enclave at the bottom of the stack is cryptographically brilliant, yet operationally blind. It has no eyes, no physical screen, and no human consciousness. It cannot tell the difference between a legitimate customer withdrawing 0.05 BTC to their cold wallet in Marseille and a North Korean hacker sitting inside a hijacked withdrawal container requesting 18,270 BTC across eleven outputs.
As long as the network packet arrives over the authenticated internal bus bearing the correct cryptographic service credentials, the MPC cluster obeys.
When Lazarus operators compromised that DevOps engineer’s laptop forty-eight hours before the heist, they did not waste a single CPU cycle trying to factor secp256k1 elliptic curves or extract key shares from the MPC nodes.
They simply rode the engineer’s ambient authority into the production container that sits upstream of the signer. Once inside the orchestration container, they owned the deputy. And because the deputy had permission to ask the vault for signatures, the vault signed away $6.36 billion without ever leaking a key.
Wall Street just panicked over an election and wiped out $2.5 trillion. But China’s AI surge proves America can’t slow down—even if the financial reckoning is just beginning.
If compromising an upstream signing container explains how the attackers initiated the theft across ten blockchains, what they did next on Ethereum reveals why adding programmable complexity to base-layer accounts is a gift to state-sponsored hackers.
**During the Pectra hard fork, Ethereum developers introduced **EIP-7702
, a specification designed to bring “Account Abstraction” to ordinary Externally Owned Accounts. Before EIP-7702
, a standard wallet address controlled by a private key could never contain executable smart-contract code; its internal codeHash
field was permanently empty. Every single time funds left that wallet, the private key had to sign a brand-new transaction.
EIP-7702
** changed the fundamental physics of the account model by introducing a** Type-4 transaction. Using this transaction type, a standard wallet can sign a special cryptographic authorization tuple—containing the chain ID, a target smart-contract address, and the account’s current transaction counter (its nonce)—that writes a delegation pointer (0xef0100
followed by the target contract address) directly into the wallet’s code storage.
Once that delegation pointer is set on-chain, the wallet is no longer just a keypair. Any external call made to that wallet automatically executes the code of the delegated smart contract—exactly like a persistent delegatecall
wearing the victim’s identity.
Now put yourself in the shoes of the Lazarus operators at 20:20 UTC on October 29 as they stared at Binance’s primary Ethereum hot wallet, known on-chain as Binance 14.
They wanted to trick Binance’s signing enclave into signing an EIP-7702
authorization that would delegate Binance 14 to their own malicious sweeper contract. However, they faced a formidable technical hurdle: because Binance 14 was actively processing legitimate user withdrawals every second, its account nonce was incrementing rapidly in real time.
**In Ethereum’s account model, an **EIP-7702
** authorization is strictly valid only if its signed nonce matches the exact nonce of the authority account at the millisecond the transaction is included in a block.**
If the attackers generated a single authorization for nonce 18,914,775, and three routine customer withdrawals confirmed a half-second earlier, the wallet’s nonce would jump to 18,914,778—rendering the attacker’s signature useless.
How did the attackers solve the moving-target problem? They weaponized the automated speed of Binance’s own signing container against it:
The Pre-Signed Volley:Inside the hijacked service container, the attackers rapidly requested50 consecutive authorizationsfrom the signing engine, spanning every single integer from nonce 18,914,775 through nonce 18,914,824.**The Bundled Payload:**At 20:20:59 UTC, they stuffed all fifty pre-signed authorization tuples into theauthorization_list
of a single Type-4 transaction and broadcast it to the Ethereum mempool.**The Fatal Hit:**When the block validator processed the list, forty-nine of the fifty authorizations failed their nonce checks and were silently skipped. One single tuple matched the live state of Binance 14 on the nose.
In that instant, without moving a single token in the setup transaction itself, Binance 14 was silently converted into a Trojan horse.
Three minutes and twenty-four seconds later, at 20:24:23 UTC, the attackers triggered their newly delegated sweeper logic. In one gulp, $2.5 billion poured out of Binance 14.
**Then came the true nightmare of **EIP-7702
. Minutes after the first drain, Binance’s automated warm-wallet rebalancing scripts noticed that Binance 14’s balance had dropped below its operational threshold. Completely unaware that the hot wallet’s underlying account code had just been mutated on-chain, the exchange’s internal bots automatically transferred hundreds of millions of dollars in fresh reserve tokens back into Binance 14 to refill the tank.
Because the EIP-7702
delegation pointer was still active inside the account state, the attackers didn’t even need access to the compromised DevOps laptop or the MPC signing container anymore!
The hijacked wallet automatically swept the incoming refills straight into the hacker’s addresses—draining Binance 14 three separate times before engineers finally severed network connections and revoked the delegation.
Now shift your gaze from Ethereum to the Bitcoin blockchain during those same twenty minutes on October 29.
While the attackers controlled Binance’s internal withdrawal container, they managed to force the signing enclave to sign eleven discrete Bitcoin transactions, extracting 18,270 BTC. That loss was a catastrophic operational failure of keeping $1.45 billion in Bitcoin wired to an online signing server.
Yet notice what the attackers could not do on Bitcoin: they could not install a persistent sweeper on Binance’s Bitcoin addresses, and they could not automatically hijack subsequent incoming deposits without continually feeding new unsigned transactions into the compromised signing container.
Why? Because seventeen years ago, Satoshi Nakamoto rejected the mutable Account Model and built Bitcoin on an entirely different mathematical foundation: the Unspent Transaction Output (UTXO) Model paired with a deliberately Turing-incomplete scripting language.
Compare how the two architectures treat the concept of ownership and state: